Certification · Information security
ISO/IEC 27001:2022 Certified Information Security You Can Check
Lenders trust us with loan and device data for thousands of borrowers. So the company that builds and runs Loksiz, Apptimate Software Private Limited, has its information security management system independently audited and certified to ISO/IEC 27001:2022, the international standard for keeping information safe.
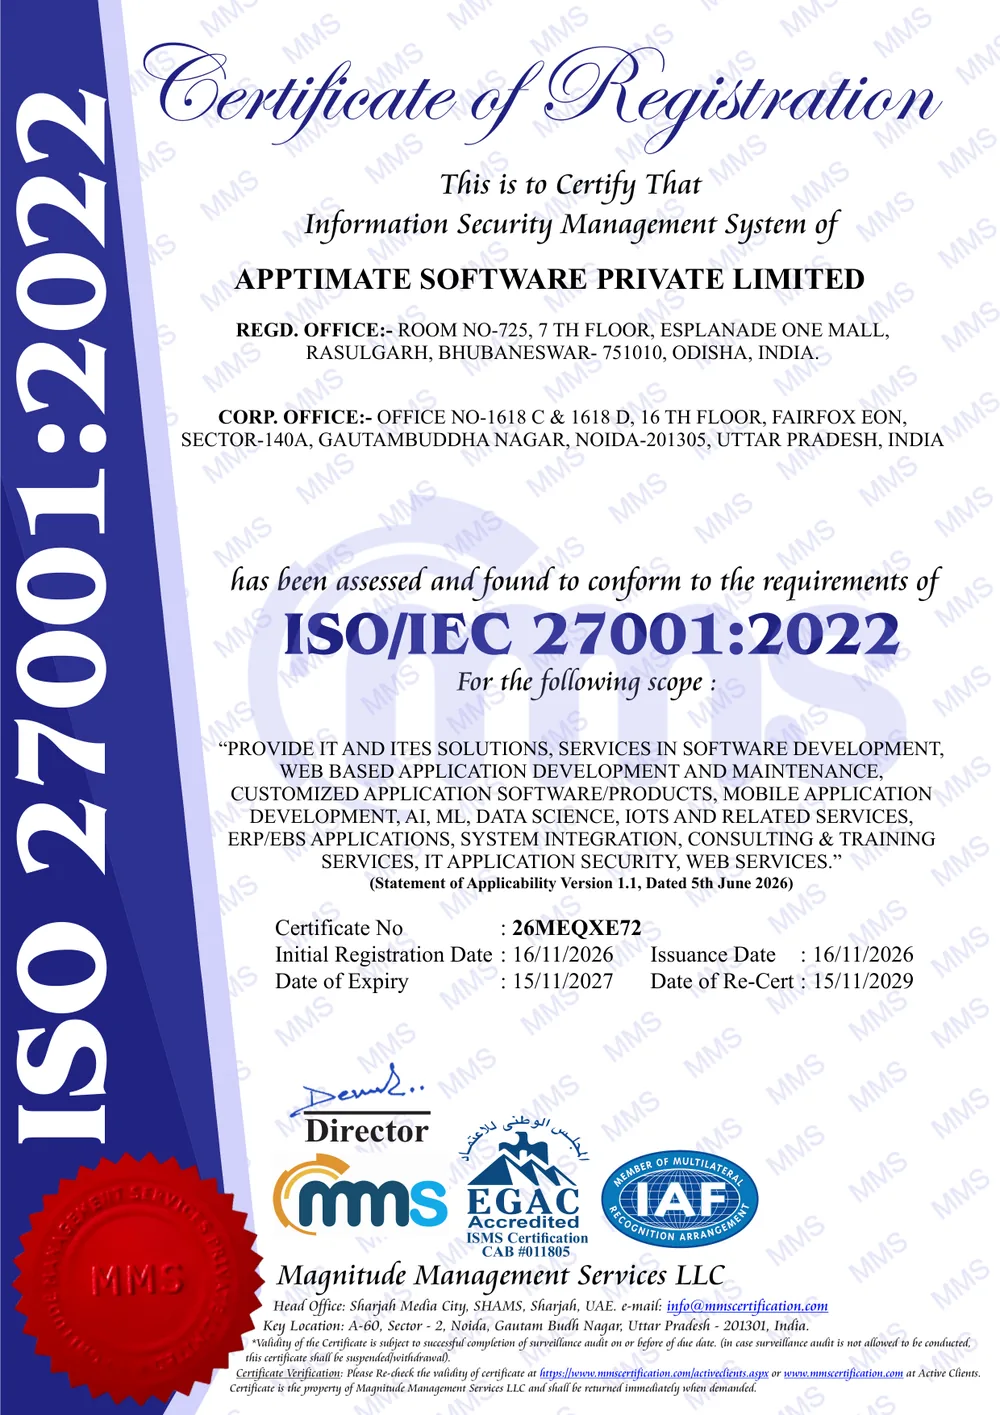
CERTIFICATE DETAILS
Everything on the Certificate
- Standard
- ISO/IEC 27001:2022, Information Security Management System
- Certificate number
- 26MEQXE72
- Certified company
- Apptimate Software Private Limited
- Certification body
- Magnitude Management Services LLC (MMS), Sharjah, UAE. Accredited by EGAC (CAB #011805), shown with the IAF MLA mark
- Initial registration
- 16 November 2026
- Current certificate valid until
- 15 November 2027, renewed after each yearly surveillance audit
- Re-certification due
- 15 November 2029
- Statement of Applicability
- Version 1.1, dated 5 June 2026
- Offices covered
- Registered office: Room No. 725, 7th Floor, Esplanade One Mall, Rasulgarh, Bhubaneswar 751010, Odisha, India. Corporate office: Office No. 1618 C and 1618 D, 16th Floor, Tower A, Fairfox EON, Sector 140A, Noida, Uttar Pradesh 201305, India
- Scope
- Provide IT and ITES solutions, services in software development, web based application development and maintenance, customized application software/products, mobile application development, AI, ML, data science, IoTs and related services, ERP/EBS applications, system integration, consulting and training services, IT application security, web services.
Check It in a Minute
- Open the MMS Active Clients page
- Search for certificate number 26MEQXE72 or “Apptimate Software”
- Check the company name, standard and dates match this page
We publish these details so you never have to take our word for it.
IN PLAIN WORDS
What ISO 27001 Actually Asks Of Us
ISO/IEC 27001 isn't a one-off checklist. It asks a company to run a management system for information security: find the risks to the information it handles, put controls in place, check they work, and keep improving. The 2022 version groups its 93 reference controls into four themes.
Organisational controls
Policies, roles, supplier security, incident handling, business continuity and legal requirements.
People controls
Screening, security awareness and training, confidentiality and remote working.
Physical controls
Secure offices and equipment, and protecting devices and storage media.
Technological controls
Access control, encryption, logging and monitoring, secure development and backups.
FOR LENDERS AND PARTNERS
What It Means If You're a Lender or Partner
- The company handling your loan and device data has had its security management checked by an outside auditor
- Security is managed as an ongoing system with yearly surveillance audits, not a one-time project
- It makes vendor due diligence quicker: you can share this certificate with your risk and compliance teams
- It sits alongside the way Loksiz is designed for RBI's device-lock rules, including not reading borrowers' personal data
 is a brand ofApptimate Software Private Limited
- CIN
U72900OR2013PTC017289- GSTIN
09AAACQ3222B1Z0- Registered office
- Room No. 725, 7th Floor, Esplanade One Mall, Rasulgarh, Bhubaneswar 751010, Odisha, India
- Corporate office
- Office No. 1618 C and 1618 D, 16th Floor, Tower A, Fairfox EON, Sector 140A, Noida, Uttar Pradesh 201305, India
Questions People Usually Ask Us
If yours isn't here, email info@loksiz.com and we'll answer it.
OUR OTHER CERTIFICATES
Certifications and Registrations
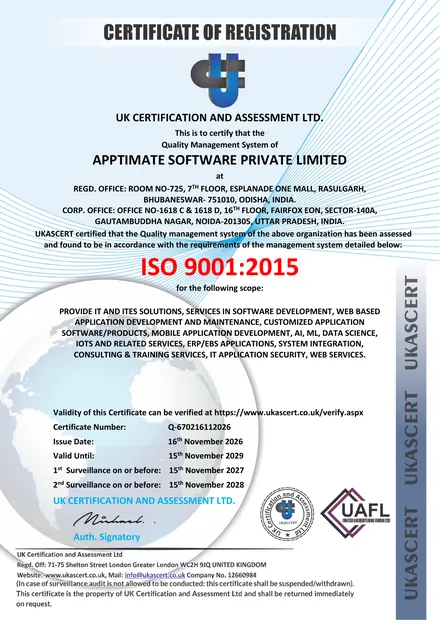
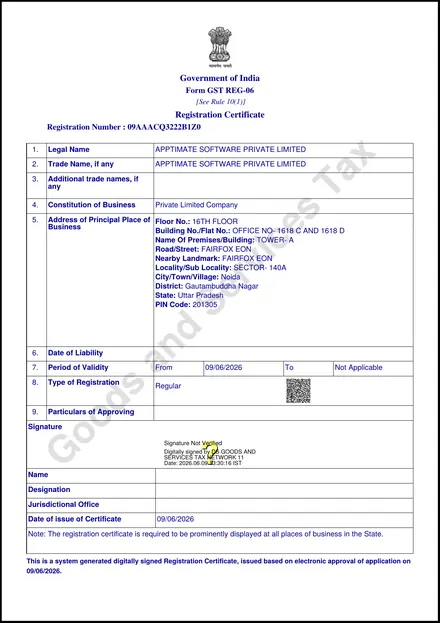
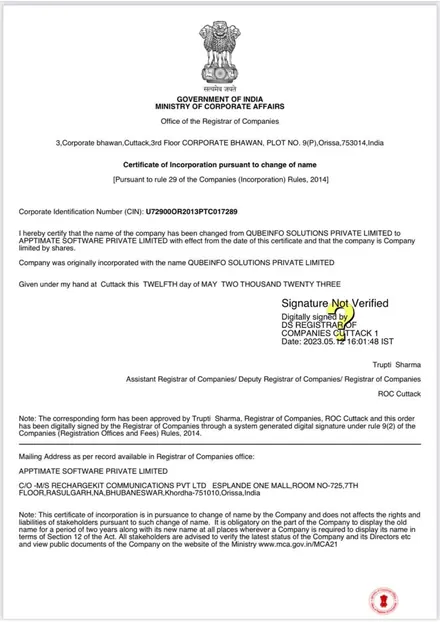
Need Documents for Vendor Due Diligence?
We'll send certificates, company details and a sample invoice for your risk and finance teams.